Recently I was troubleshooting an environment where Windows 10 upgrades didn't came in. I did check if hotfixes were installed, which was the situation indeed.
-KB3095113: Update to enable WSUS support for Windows 10 feature upgrades (Server 2012 and 2012R2)
-KB3127032: Windows 10 upgrades are not downloaded in System Center Configuration Manager (CM1511 only)
I decided to remove the Upgrade checkbox, too put it on at later time. Then a new pop-up was displayed: Additionally, to service Windows 10 Version 1607 and later, you must install and configure KB3159706 using the guidance. Oops, I missed that one! Installed it a the WSUS/SUP and other Site server(s) and did have a look at additional steps too. This because of the following post on Microsoft TechNet: WSUS Breaks after KB3159706, released 5/5/2016
It mentions: Manual steps required to complete the installation of this update:
1. Install the hotfix and restart the WSUS/SUP server!
2. Open an elevated Command Prompt window, and run "C:\Program Files\Update Services\Tools\wsusutil.exe postinstall /servicing" (case sensitive)
3. Select HTTP Activation under .NET Framework 4.5 Features in the Server Manager Add Roles and Features wizard.
4. Restart the WSUS service.
I skipped steps mentioned on "If SSL is enabled on the WSUS server" at first try, but they seems to be needed too!
1.Open an elevated Command Prompt window, and assign ownership of the Web.Config file to the administrators group
-takeown /f web.config /a
-icacls "C:\Program Files\Update Services\WebServices\ClientWebService\Web.config" /grant administrators:f
2. Make the following changes in the file > add the lines displayed in bold, don't make the mistake (as me) to replace those lines!
3. Add the multipleSiteBindingsEnabled="true" attribute to the bottom of the Web.Config file
4. Restart the WSUS service.
Start a Software Update sync in ConfigMgr and watch wsyncmgr.log and WCM.log closely. Everything should be fine now!
Didn't see Windows 10 Servicing working yet, but hope too see it in near future. On Microsoft Ignite there was no session or demo about it too, given the fact that it may be working.
Will be continued in a next blogpost :-)
Showing posts with label Servicing. Show all posts
Thursday, October 6, 2016
Enable the Upgrades classification in ConfigMgr Current Branch (again)
Wednesday, September 28, 2016
Now Available: Update 1609 for ConfigMgr Technical Preview
Today (September 27th) the latest ConfigMgr (preview) version is released: Update 1609 for ConfigMgr Technical Preview. Update 1609 for Technical Preview is available directly in the ConfigMgr console. If you want to install ConfigMgr Technical Preview for the first time, the installation bits (currently based on Technical Preview 1603) are available on TechNet Evaluation Center. The new version offers lots of new functionality, with several great new features.
This update includes the following improvements:
-Windows 10 Upgrade Analytics (assess and analyze device readiness and compatibility with Windows 10 to allow smoother upgrades)
-Office 365 Client Management Dashboard (track Office 365 updates and deployments)
-Deploy Office 365 apps to clients (Office 365 Servicing node in Software Library, deploy Office 365 apps to clients)
-Improvements for BIOS to UEFI conversion (OS deployment task sequence with a new variable, called TSUEFIDrive)
-Improvement to Endpoint Protection antimalware policy settings (specify the level to block suspicious files)
-Boundary Group Improvements (more granular control of fallback behavior, and greater clarity which DP's are used)
This update also includes new features for customers using ConfigMgr integrated with Intune (hybrid scenario):
-TouchID, ApplePay and Zoom DEP Settings (create enrollment profiles to skip initial setup screens for new iOS devices)
-Windows Store for Business (allows customers to obtain applications, purchased or free, and deploy them to users)
-Android, iOS, and Windows Additional Settings (create Windows 10 VPN profiles without using OMA-URI)
-Intune Compliance Charts (quick view of overall device compliance, and top reasons for non-compliance using new charts)
And nested task sequences will be available soon too! Just great a new (preview) version is available now! Happy installing :-)
Source: Enterprise Mobility and Security Blog
Detailed overview of new features: Microsoft TechNet
Wednesday, September 7, 2016
Update Rollup 1 for ConfigMgr Current Branch, version 1606 available now!
Today the following ConfigMgr update is released: Update Rollup 1 for ConfigMgr Current Branch, version 1606. It fixes 16 issues and 1 additional change is included. It sounds like a cumulative update with many improvements to me :) Let's have a look at the fixes.
This update includes the following improvements:
-Administrator Console (1 fix)
-Updates and servicing (1 fix)
-Client (4 fixes)
-Software Updates (2 fixes)
-Site Systems (1 fix)
-Operating System Deployment (1 fix)
-Windows Store for Business (4 fixes)
-Software distribution and content management (1 fix)
-Endpoint Protection (1 fix)
Additional changes included in this update:
-Windows Server 2016 is now available in the supported platform list for Content Distribution, Software Update Management, and Settings Management.
This update is available for installation in the Updates and Servicing node of the ConfigMgr console. If the service connection point is in offline mode, you have to re-import the update so that it is listed in the ConfigMgr console. Refer to Install Updates for System Center Configuration Manager for details.
For more details and to view the full list of new features in this update check out our documentation on TechNet.
Wednesday, August 24, 2016
Doing an in-place upgrade from Windows 10 Build 1511 to 1607
This month Windows 10 Build 1607 (Anniversary update) is released. This is the third Windows 10 Build, next to 1507 (RTM) and 1511 (November update). Where servicing within ConfigMgr wasn't possible from 1507 to 1511, this is possible now. Expect some notes from the field soon, where systems in my company will be updated from 1511 to 1607. Hope to have some good results again :)
From a customer I got some update cons already. Let's have a look at few disappointments so far:
-Drivers working in 1511 doesn't have to be working in 1607. Maybe some hardware must be replaced, because it's not supported anymore. Think about some VGA or NIC drivers;
-Universal apps removed in the Operating System before, will be back after an in-place upgrade. They must be removed in the image before upgrading or removed again after the upgrade;
-Default apps set for Webbrowser, Email or PDF (for example) will be reset after an in-place upgrade. They must be configured again after the upgrade or set by an User Environment solution;
But the hardest thing: some Group Policy set in Pro edition earlier, is available for Enterprise edition only now.
-Configure Spotlight on lock screen
-Turn off all Windows Spotlight features
-Turn off Microsoft Consumer features
-Do not display the lock screen
-Do not require CTRL+ALT+DELETE & Turn off app notifications on the lock screen
-Do not show Windows Tips
-Force a specific default lock screen image
-Start Menu layout
-Turn off the Store application
-Only display private store within the Windows Store app
-Don't search the web or display web results
So when using Pro 1511 already, and you want to manage some features above, you need Enterprise 1607 in future. That's the biggest disappointment for some companies I guess.
Hope to experience the in-place upgrade myself soon. On two home systems I did an rollback earlier because of driver malfunction. There will be some benefits added later too I guess :)
Sources:
Group Policies that apply only to Windows 10 Enterprise and Education Editions
Update 25-8: Windows 10 users moving from version 1511 to version 1607, dubbed the "anniversary update," may find applications installed on their systems that they'd previously removed.
Windows 10 Anniversary Update Restores Deleted Apps
Windows 10 1607: Keeping apps from coming back when deploying the feature update
Tuesday, July 26, 2016
Now Available: Update 1606 for ConfigMgr Current Branch
Last week (July 22th) the following ConfigMgr version is released: Update 1606 for ConfigMgr Current Branch. With this update new update functionality in ConfigMgr Current Branch can be used finally. No need to install servicepacks or cumulative updates anymore. Just make sure there's a recent back-up and install this version.
This update includes the following improvements:
-Windows Information Protection (formerly EDP)
-Windows Defender Advanced Threat Protection
-Windows Store for Business Integration
-Windows Hello for Business
We’ve also added a number of popular User Voice items, including:
-The addition of content status links in the admin console
-The option of list view for applications in the Software Center
-The ability to select multiple updates and simultaneously install them with the new Install Selected Updates button in the Software Center
For more details and to view the full list of new features in this update check out our documentation on TechNet.
Just great a new version is available now!
Source: ConfigMgr Team Blog
Tuesday, June 21, 2016
Now Available: Update 1606 for ConfigMgr Technical Preview
Today (June 21th) the latest ConfigMgr (preview) version is released: Update 1606 for ConfigMgr Technical Preview. Update 1606 for Technical Preview is available directly in the ConfigMgr console. If you want to install ConfigMgr Technical Preview for the first time, the installation bits (currently based on Technical Preview 1603) are available on TechNet Evaluation Center.
This update includes the following improvements:
-ConfigMgr as a managed installer with Device Guard (ConfigMgr-deployed software is automatically trusted)
-Cloud Proxy Service (manage ConfigMgr clients on the Internet, with an Azure subscription)
-Grace period for application and software update deployments (give users a grace period to install required applications or software updates)
-Multiple device management points for Windows 10 Anniversary Edition devices (automatically configures an enrolled device to have more than one device management point available for use)
This update also includes new features for customers using ConfigMgr integrated with Intune (hybrid scenario):
-Device categories (automatically place devices in device collections when used in hybrid environments)
Hope that nested task sequences will be available soon too!
Just great a new (preview) version is available now!
Source: Enterprise Mobility and Security Blog
Monday, May 30, 2016
Defer Windows 10 upgrades in Group Policy and ConfigMgr Current Branch
With Windows 10 in enterprises, it's recommended to devide systems between Current Branch (CB) and Current Branch for Business (CCB). Where few systems will be in CB for testing new functionalities, most systems will be in CBB probably. Difference is a 4 months delay for new Windows 10 builds, which can be extended for another 8 months to have a 12 months delay in total. After 1 year you're out of support, and no security updates will be offered anymore.
To divide systems between CB and CBB, Group Policy and/or ConfigMgr can be used. Within the new group policy templates, the following settings is available: Defer Upgrades and Updates
When this policy is enabled and linked, a 4 months delay is the result. This can be extended for another 8 months on upgrades and 4 weeks on updates. You can pause upgrades and updates too. Nothing wrong with that.
When using ConfigMgr Current Branch things get a bit different. Now you have a Windows 10 Servicing dashboard and CB is called Release Ready (RR). CBB is called Business Ready (BR) here. Why using different terms here is not handy and not logical to me. It's also not easy to move systems from RR to BR. Therefore lot's of prerequisites must be in place.
When looking on: Manage Windows as a service using System Center Configuration Manager you will see the prerequisites:
- Windows 10 computers must use ConfigMgr software updates with WSUS for software update management
- WSUS 4.0 with KB3095113 must be installed on your software update points and site servers
-Enable Heartbeat Discovery (7 days by default)
-The service connection point must be installed and configured for Online, persistent connection mode to see data on the Windows 10 servicing dashboard
-Specify the group policy setting, Defer Upgrades and Updates, to determine whether a computer is CB or CBB
-IE9 or later must be installed on the computer that runs the Configuration Manager console
-Software updates must be configured and synchronized
Strange thing is however, you need to configure group policy and a servicing plan too. Here you can choose between CB or CBB and there's a delay of 120 days possible. This is around 4 months, and not the same as the 8 months which can be configured in group policy. Why the difference here, on days instead of months?
On Manage Windows as a service using System Center Configuration Manager you will see the following on that: "How many days after Microsoft has published a new upgrade would you like to wait before deploying in your environment". Maybe I want to wait 12 months, how to configure that? Hope that someone or Microsoft can clarify something on that.
For now I see most environments with systems in CB/RR without the possibility to move them to CBB/BR easily.
Request: Besides of that I want to click on the dashboard, to see which systems has which build installed and which ring is configured. That will has benefit above off the value displayed.
Will be continued..
Wednesday, March 16, 2016
Upgrade ConfigMgr Current Branch to build 1602 (installation steps)
In an earlier blogpost I wrote about the prerequisite check. It can be found HERE. This time I will show the installation steps. It's really easy, so just run "Install Update Pack" and be amazed :-)
The following screens will be shown:
And a few other screens which are less important to show (License Terms, Summary, Completion).
During installation progress is shown in CMUpdate.log (within the ConfigMgr\Logs folder).
When installation is finished you get a message that the ConfigMgr console needs to be closed (when opened) for update reasons. The installation is almost done now.
The upgrade is finished soon, and the console will be opened automatically again. Check Sitecomp.log (within the ConfigMgr\Logs folder again) for more information.
Just great to install future ConfigMgr updates this way! By far the easiest upgrade ever :-)
The following screens will be shown:
General information
Select Features
Client update options
And a few other screens which are less important to show (License Terms, Summary, Completion).
During installation progress is shown in CMUpdate.log (within the ConfigMgr\Logs folder).
When installation is finished you get a message that the ConfigMgr console needs to be closed (when opened) for update reasons. The installation is almost done now.
The upgrade is finished soon, and the console will be opened automatically again. Check Sitecomp.log (within the ConfigMgr\Logs folder again) for more information.
Just great to install future ConfigMgr updates this way! By far the easiest upgrade ever :-)
Tuesday, March 15, 2016
Upgrade ConfigMgr Current Branch to build 1602 (prerequisite check)
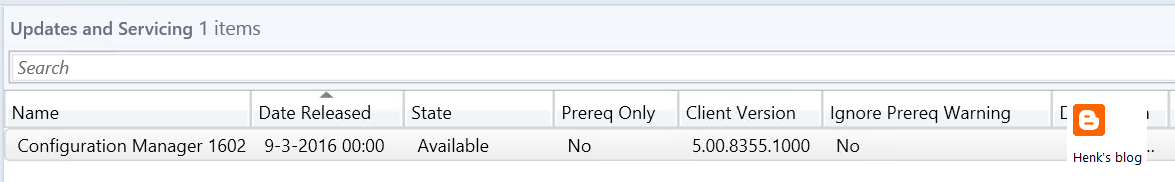
This week I did an upgrade of ConfigMgr Current Branch (1511) to build 1602. Where updates before were based on service packs or cumulative updates, this one is done through the Service connection point. When no update is seen in the console, download the script EnableUpdateRing, which will activate it. (Right click and Save As to download. Rename the .txt extension to .ps1 after downloading)
- Run the ps1 script EnableUpdateRing
- New updates are checked for every 24h so if you don't see it yet, restart SMS_DMP_Downloader service from ConfigMgr Service Manager.
- Monitor download from dmpdownloader.log
- Run Update from Updates and Servicing
In my situation the download started immediately after running the script and restarting the service.
After that content is downloaded to the ConfigMgr\EasySetupPayLoad folder.
IMPORTANT NOTE: As a temporary workaround if the update installation is suspended at “Downloading” state for extended period of time, restart the SMS_EXECUTIVE (smsexec) service on the standalone primary or central administration site server (CAS).
When download is complete the status will be changed to Available.
When rightclick on "Install Update Pack" or "Run prerequisite check" you can start right away. I did run the prereq check first, which gave me an error on free disk space. There was around 12,4GB free space, but apparently this was not enough?
[Failed]:Checks that the site server computer has sufficient available disk space to install the site server.
Therefore I added 25GB extra disk space and after that the prereq check was running fine. So next time make sure you have free disk space enough on the drive where ConfigMgr is installed :-)
When prereqs are fine you can go further with installing the update pack. Stay tuned for more soon!
Monday, March 14, 2016
Now Available: Update 1602 for ConfigMgr Current Branch
Last week (March 11th) the following ConfigMgr version is released: Update 1602 for ConfigMgr Current Branch. With this update new update functionality in ConfigMgr Current Branch can be used finally. No need to install servicepacks or cumulative updates anymore. Just make sure there's a recent back-up and install this version.
This update includes the following improvements:
-Client Online Status
-Support for SQL Server AlwaysOn Availability Groups
-Windows 10 Device Health Attestation Reporting
-Office 365 Update Management
-New Antimalware Policy Settings
This update also includes new features for customers using ConfigMgr integrated with Intune (hybrid scenario):
-Conditional Access for PC's Managed by ConfigMgr
-Windows 10 Conditional Access Enhancements
-Microsoft Edge Configuration Settings
-Windows 10 Team Support
-Apple Volume Purchase Program (VPP) Support
-iOS App Configuration
-iOS Activation Lock Management
-Kiosk Mode for Samsung KNOX Devices
-User Acceptance of Terms and Conditions
For more details and to view the full list of new features in this update check out our documentation on TechNet.
Just great a new version is available now!
Source: ConfigMgr Team Blog
Subscribe to:
Posts (Atom)